I’m running the latest QubesOS and i’m up to date with Dom0. I tried using Xen kernel boot parameters ssbd=1 or spec-ctrl=ssbd however it says i’m still vulnerable eventhough I have the capability to mitigate it.
Confirm by typing at Dom0 terminal, sorry no screenshot: “cat /sys/devices/system/cpu/vulnerabilities/spec_store_bypass
Vulnerable”
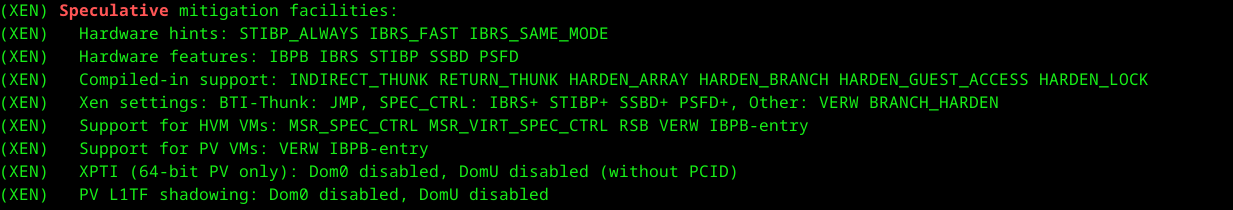
I thought this was fixed a long time ago `spectre-meltdown-checker` reports `CVE-2018-3639 aka 'Variant 4, speculative store bypass'` · Issue #9432 · QubesOS/qubes-issues · GitHub
Forgot to mention when using Secureblue OS on the same computer the SSB is mitigated.
Does anyone know any Xen kernel boot parameters that actually works to mitigate SSB vulnerability?